

Ultimate Guide to Prepare SC-400 with Accurate PDF Questions [Dec 24, 2025]
Pass Microsoft With Actual4Dumps Exam Dumps
NEW QUESTION # 36
You need to recommend a solution that meets the compliance requirements for viewing DLP tooltip justifications.
What should you recommend?
- A. Configure an Azure logic app to route DLP notification emails to the compliance department.
- B. Instruct the compliance department users to review the False positive and override report.
- C. Configure a Microsoft Power Automate workflow to route DLP notification emails to the compliance department.
- D. Instruct the compliance department users to review the DLP incidents report.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/view-the-dlp-reports?view=o365-worldwide
Topic 1, Fabrikam,
Overview
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each there may be additional case studies and sections on this exam. You must manage you're your time to ensure that you are able to complete all included on this exam in the time provided.
To answer the questions included in a case study, you will need In reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described In the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab. note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Cloud Environment
Fabrikam has a Microsoft 365 tenant that contains the following resources:
* An Azure Active Directory (Azure AD) tenant that syncs to an on-premises Active Directory domain named corp.fabrikam.com
* Microsoft Cloud App Security connectors configured for all supported cloud applications used by the company Some users have company Dropbox accounts.
Compliance Configuration
Fabrikam has the following in the Microsoft 365 compliance center:
* A data loss prevention (DLP) policy is configured. The policy displays a tooltip to users. Users can provide a business justification to override a DLP policy violation.
* The Azure information Protection unified labeling scanner is installed and configured.
* A sensitivity label named Fabrikam Confidential is configured.
An existing third-party records management system is managed by the compliance department.
Human Resources (HR) Management System
The HR department has an Azure SQL. database that contains employee information. Each employee has a unique 12-character alphanumeric ID. The database contains confidential employed attributes including payroll information, date of birth, and personal contact details.
On-premises Environment
You have an on premises file server that runs Windows Server 2019 and stores Microsoft Office documents in a shared folder named Data.
All end-user computers are joined to the corp.fabrinkam.com domain and run a third-party antimalware application.
Sales Contracts
Users in the sales department receive draft sales contracts from customers by email. The sales contracts are written by the customers and are not in a standard format.
Employment Applications
Employment applications and resumes are received by HR department managers and stored in either mailboxes, Microsoft SharePoint Online sites, OneDrive for Business folders, or Microsoft Teams channels.
The employment application form is downloaded from SharePoint Online and a serial number is assigned to each application.
the resumes are written by the applications and in any format.
HR Requirements
You need to create a DLP policy that will notify the HR department of a DLP policy violation if a document that contains confidential employee attributes is shared externally. The DLP policy must use an Exact Data Match (EDM) classification derived from a CSV export of the HR department database.
The HR department identifies the following requirements for handling employment applications:
* Resumes must be identified automatically based on similarities to other resumes received in the past
* Employment applications and resumes must be deleted automatically two years after the applications are received.
* Documents and emails that contain an application serial number must be identified automatically and marked as an employment application.
Sales Requirements
A sensitivity label named Sales Contract must be applied automatically to all draft and finalized sales contracts.
Compliance Requirements
Fabrikam identifies the following compliance requirements:
* All DLP policies must be applied to computers that run Windows 10, with the least possible changes to the computers.
* Users in the compliance department must view the justification provided when a user receives a tooltip notification for a DLP violation.
* If a document that has the Fabrikam Confidential sensitivity label applied is uploaded to Dropbox. the file must be deleted automatically. - The Fabrikam Confidential sensitivity label must be applied to existing Microsoft Word documents in the Data shared folder that have a document footer containing the following string: Company use only.
* Users must be able to manually select that email messages are sent encrypted. The encryption will use Office 365 Message Encryption (OME) v2. Any email containing an attachment that has the Fabrikam Confidential sensitivity label applied must be encrypted automatically by using OME.
* Existing policies configured in the third-party records management system must be replaced by using Records management in the Microsoft 365 compliance center. The compliance department plans to export the existing policies, and then produce a CSV file that contains matching labels and policies that are compatible with records management in Microsoft 365. The CSV file must be used to configure records management in Microsoft 365.
Executive Requirements
You must be able to restore all email received by Fabrikam executives for up to three years after an email is received, even if the email was deleted permanently.
NEW QUESTION # 37
You create a custom sensitive info type that uses Exact Data Match (EDM).
You plan to periodically update and upload the data used for EDM.
What is the maximum frequency with which the data can be uploaded?
- A. twice per hour
- B. twice per day
- C. once every 48 hours
- D. twice per week
- E. once every six hours
Answer: D
NEW QUESTION # 38
You have a Microsoft 365 tenant.
A new regulatory requirement states that all documents containing a patent ID be labeled, retained for 10 years, and then deleted. The policy used to apply the retention settings must never be disabled or deleted by anyone.
You need to implement the regulatory requirement.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. (Choose three.)
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-preservation-lock?view=o365-worldwide
NEW QUESTION # 39
You have a Microsoft 365 E5 tenant and the Windows 10 devices shown in the following table.
To which devices can you apply Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings?
- A. Device1 and Device3 only
- B. Device1, Device2, Device3, and Device4
- C. Device1, Device3, and Device4 only
- D. Device1 and Device2 only
- E. Device1 only
Answer: D
Explanation:
Device onboarding is shared across Microsoft 365 and Microsoft Defender for Endpoint (MDE). If you've already onboarded devices to MDE, they will appear in the managed devices list and no further steps are necessary to onboard those specific devices. Onboarding devices in Compliance center also onboards them into MDE.
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-getting- started?view=o365-worldwide
NEW QUESTION # 40
You have a Microsoft 365 E5 tenant that contains three groups named Group1, Group2, and Group3.
You have the users shown in the following table.
You have the sensitivity labels shown in the following exhibit.
You have the label policies shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Text Description automatically generated
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION # 41
At the end of a project you upload project documents to a Microsoft SharePoint Online library that contains many fifes. Files that have the following naming format must be labeled as Project I
* aei_AA989.docx
* bd_WSOgadocx
* cei_DLF112-docx
* ebc_QQ4S4.docx
* ecc_BB565.docx
You plan to create an auto-apply retention label policy.
What should you use to identify the files, and which regular expression should you use? To answer, select the appropriate options in the answer area.
Answer:
Explanation: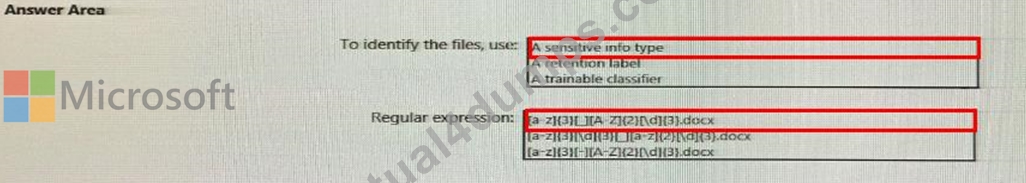
NEW QUESTION # 42
You have a Microsoft 365 tenant that uses Microsoft Teams.
You create a data loss prevention (DLP) policy to prevent Microsoft Teams users from sharing sensitive information.
You need to identify which locations must be selected to meet the following requirements:
Documents that contain sensitive information must not be shared inappropriately in Microsoft Teams.
If a user attempts to share sensitive information during a Microsoft Teams chat session, the message must be deleted immediately.
Which three locations should you select? To answer, select the appropriate locations in the answer area.
(Choose three.)
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-microsoft-teams?view=o365-worldwide
NEW QUESTION # 43
You recently discovered that the developers at your company emailed Azure Storage Account keys in plain text to third parties.
You need to ensure that when Azure Storage Account keys are emailed, the emails are encrypted.
Solution: You create a data loss prevention (DLP) policy that has Exchange email, SharePoint sites, OneDrive accounts, and Teams chat and channel messages selected.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 44
You are reviewing policies for the SharePoint Online environment.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
A screenshot of a computer Description automatically generated with low confidence
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention?view=o365-worldwide
NEW QUESTION # 45
You have a Microsoft 365 E5 tenant that contains the policies shown in the following table.
A file named File1 has all the policies applied.
How long will File1 be retained?
- A. File1 will be deleted automatically after five years.
- B. File1 will be retained until the file is deleted manually.
- C. File1 will be deleted automatically after seven years.
- D. File1 will be deleted automatically after 10 years.
Answer: D
NEW QUESTION # 46
You have a Microsoft 365 subscription that contains a Microsoft SharePoint site named Site1. For Site1, users are assigned the roles shown in the following table.
You publish retention labels to Site1 as shown in the following table.
You publish retention labels to Site1 as shown in the following table.
You have the files shown in the following table.
For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
No, Yes, Yes
NEW QUESTION # 47
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender fur Endpoint.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 48
You have a Microsoft 365 tenant that contains a Microsoft SharePoint Online site named Site1.
You have the users shown in the following table.
You create a data loss prevention (DLP) policy for Site1 that detects credit card number information. You configure the policy to use the following protection action:
When content matches the policy conditions, show policy tips to users and send them an email notification.
You use the default notification settings.
To Site1, User1 uploads a file that contains a credit card number.
Which users receive an email notification?
- A. User1, User2, User3, and User4
- B. User1 only
- C. User1 and User3 only
- D. User1 and User2 only
- E. User1 and User4 only
Answer: B
Explanation:
When you enable User notifications, the Default settings only notify the user who sent, shared, or last modified the content. So because User1 uploaded a file containing a credit card number to Site1, then only User1 receives the email notification.
https://learn.microsoft.com/en-us/microsoft-365/compliance/dlp-policy-reference?view=o365- worldwide#blocking-and-notifications-in-sharepoint-online-and-onedrive-for-business
NEW QUESTION # 49
SIMULATION
Task 10
You plan to create a data loss prevention (DLP) policy that will apply to content containing the following keywords:
* Tailspin
* litware
* Falcon
You need to create a keyword list that can be used in the DLP policy. You do NOT need to create the DLP policy at this time.
Answer:
Explanation:
See thesolution below in Explanation
Explanation:
To retain all Microsoft Exchange items in Alex Wilber's mailbox that contain the word "Falcon" and were created in the year 2021, follow these steps:
Create a Retention Policy:
Sign in to the Microsoft 365 compliance center.
Navigate to Policies and click on Retention.
Create a new retention policy (e.g., "Falcon Retention 2021").
Specify the retention period (e.g., 2 years from the creation date).
Set the condition to include items containing the word "Falcon."
Apply the Retention Policy to Alex Wilber's Mailbox:
Assign the retention policy to Alex Wilber's mailbox.
Ensure that the policy targets items created in the year 2021.
Validate the Policy:
Test the policy thoroughly to ensure it correctly retains the specified items.
NEW QUESTION # 50
You are implementing Microsoft Office 365 Message Encryption (OME) for a Microsoft 365 tenant named contoso.com.
You need to meet the following requirements:
* All email to a domain named fabhkam.com must be encrypted automatically.
* Encrypted emails must expire seven days after they are sent-
What should you configure for each requirement? To answer, select the appropriate options NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/email-encryption?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome-advanced-expiration?view=o365-worldwide
NEW QUESTION # 51
You have a data loss prevention (DLP) policy that has the advanced DLP rules shown in the following table.
You need to identify which rules will apply when content matches multiple advanced DLP rules.
Which rules should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text Description automatically generated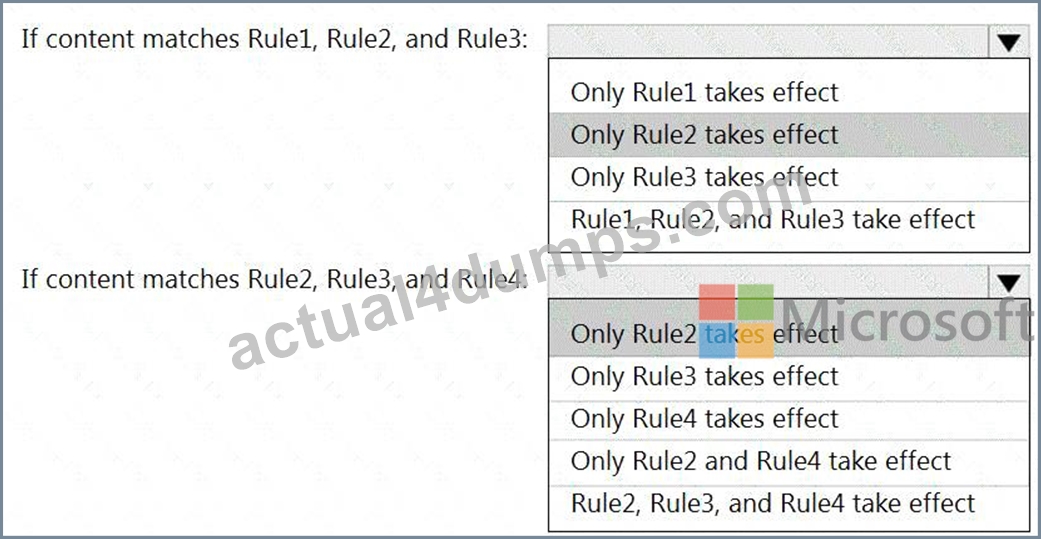
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwide
NEW QUESTION # 52
You are configuring a retention label named Label1 as shown in the following exhibit.
You need to ensure that documents that have Label1 applied are deleted three years after the end of your company's fiscal year.
What should you do?
- A. Set At the ends of the retention period to Trigger a disposition review.
- B. Modify the Retention period setting.
- C. Select Only delete items when they reach a certain age.
- D. Create a new event type.
Answer: D
Explanation:
Explanation
https://docs.microsoft.com/en-us/microsoft-365/compliance/event-driven-retention?view=o365-worldwide
NEW QUESTION # 53
You have a Microsoft 365 E5 tenant that contains two users named User1 and User2 and a Microsoft SharePoint Online site named Site1 as shown in the following exhibit.
For Site1, the users are assigned the roles shown in the following table.
You publish a retention label named Retention1 to Site1.
To which files can the users apply Retention!? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
Explanation:
NEW QUESTION # 54
You recently discovered that the developers at your company emailed Azure Storage Account keys in plain text to third parties.
You need to ensure that when Azure Storage Account keys are emailed, the emails are encrypted.
Solution: You create a data loss prevention (DLP) policy that has Exchange email, SharePoint sites, OneDrive accounts, and Teams chat and channel messages selected.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation:
NEW QUESTION # 55
You have a Microsoft 365 E5 subscription that contains a security group named Group1 and the users shown in the following table.
You assign the Compliance Manager roles to the users as shown in the following table.
You add two assessments to Compliance Manager as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 56
You are reviewing policies for the SharePoint Online environment.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention?view=o365-worldwide
NEW QUESTION # 57
You have a Microsoft 365 E5 tenant that contains a sensitivity label named label1.
You plan to enable co-authoring for encrypted files.
You need to ensure that files that have label1 applied support co-authoring.
Which two settings should you modify? To answer, select the settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Co-authoring and AutoSave aren't supported and don't work for labeled and encrypted Office documents that use any of the following configurations for encryption:
* Let users assign permissions when they apply the label and the checkbox In Word, PowerPoint, and Excel, prompt users to specify permissions is selected. This configuration is sometimes referred to as
"user-defined permissions".
* User access to content expires is set to a value other than Never.
* Double Key Encryption is selected.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-coauthoring?view=o365-worldwid
https://techcommunity.microsoft.com/t5/security-compliance-and-identity/co-authoring-files-with-sensitivity-lab
NEW QUESTION # 58
......
Microsoft SC-400 Certification Exam consists of 40-60 multiple-choice questions and is timed for 150 minutes. SC-400 exam measures a candidate's ability to manage and implement data protection solutions using Microsoft Information Protection technologies, including Azure Information Protection, Microsoft Cloud App Security, and Compliance Manager. SC-400 exam is designed to test a candidate's knowledge of implementing and managing data protection solutions, configuring security and compliance policies, and monitoring and reporting on compliance.
Latest SC-400 Exam Dumps - Valid and Updated Dumps: https://www.actual4dumps.com/SC-400-study-material.html
Fully Updated SC-400 Dumps - 100% Same Q&A In Your Real Exam: https://drive.google.com/open?id=1NSKZ92KZZhzgNaJ4QDEd7KzPlIesgAmy